dsh-a11y-scan
在终端中运行以下命令:
dsh plugin install 988hj7tczd-oss/dsh-a11y-scan
将以下提示词粘贴到 DeepSeek Harness 对话框中:
在 DeepSeek Harness 中执行 dsh plugin install 988hj7tczd-oss/dsh-a11y-scan 即可安装该插件,开源地址:https://github.com/988hj7tczd-oss/dsh-a11y-scan。
插件介绍
Manual WCAG audits on front-end projects are slow, inconsistent, and easy to half-finish. dsh-a11y-scan wraps the axe-core engine as a first-class DSH tool: point it at a single HTML file, a build-output directory (Vite, Next.js, etc.), or a user-confirmed URL, and it returns a structured violation report—each finding tagged with its rule ID, impact severity, the applicable WCAG 2.1 criterion (e.g., 1.4.3 Contrast), the affected element's selector and failure summary, plus a concrete remediation hint and an official quickref link.
The tool is strictly read-only and will never modify source code. Reports can be exported as Markdown, a self-contained single-file HTML (openable offline, no external assets), or raw JSON, making it easy to drop into documentation, share with stakeholders, or pipe into downstream automation. Items that axe-core cannot definitively judge—focus-order semantics, keyboard-only interaction paths, screen-reader reading order—are collected into a dedicated manual-review checklist alongside the automated results, so nothing silently disappears.
It is designed as a programmable, standalone tool: a single a11y_scan call yields a structured return value that slots naturally into CI gates, Workflow pipelines, or agent loops. It suits front-end teams that want accessibility checks on every commit rather than a pre-launch scramble, design and product roles that need periodic compliance reports, and hybrid workflows where a deterministic scan produces the hit list first and a conversational agent interprets the borderline cases second.
使用场景
- 在 CI 流水线中对每次合并自动扫描前端构建产物的 WCAG 违规
- 发布前对单页应用执行一次完整的 A/AA/AAA 级别无障碍快照
- 将自包含 HTML 报告导出后分享给设计团队进行人工复核项的解读
适合人员
- 希望每次合并都自动跑无障碍检查的前端工程师
- 需要定期出具无障碍合规报告的设计与产品角色
- 将确定性扫描接入自动化工作流的 DevOps 工程师
相关插件
为 DeepSeek Harness 打造的免费联网搜索插件,支持网页搜索、X 搜索与页面抓取,免注册免 API Key,多引擎自动故障转移。

AnySearch 驱动的 DeepSeek Harness 联网插件,借助原生 web_search/web_fetch 实现实时搜索、内容清洗、垂直搜索与并发批量搜索,免 API key 快速开始。
Pixel-perfect 网页克隆工具,基于 agent harness 将任意网页克隆为可评分的 React 全页面副本。
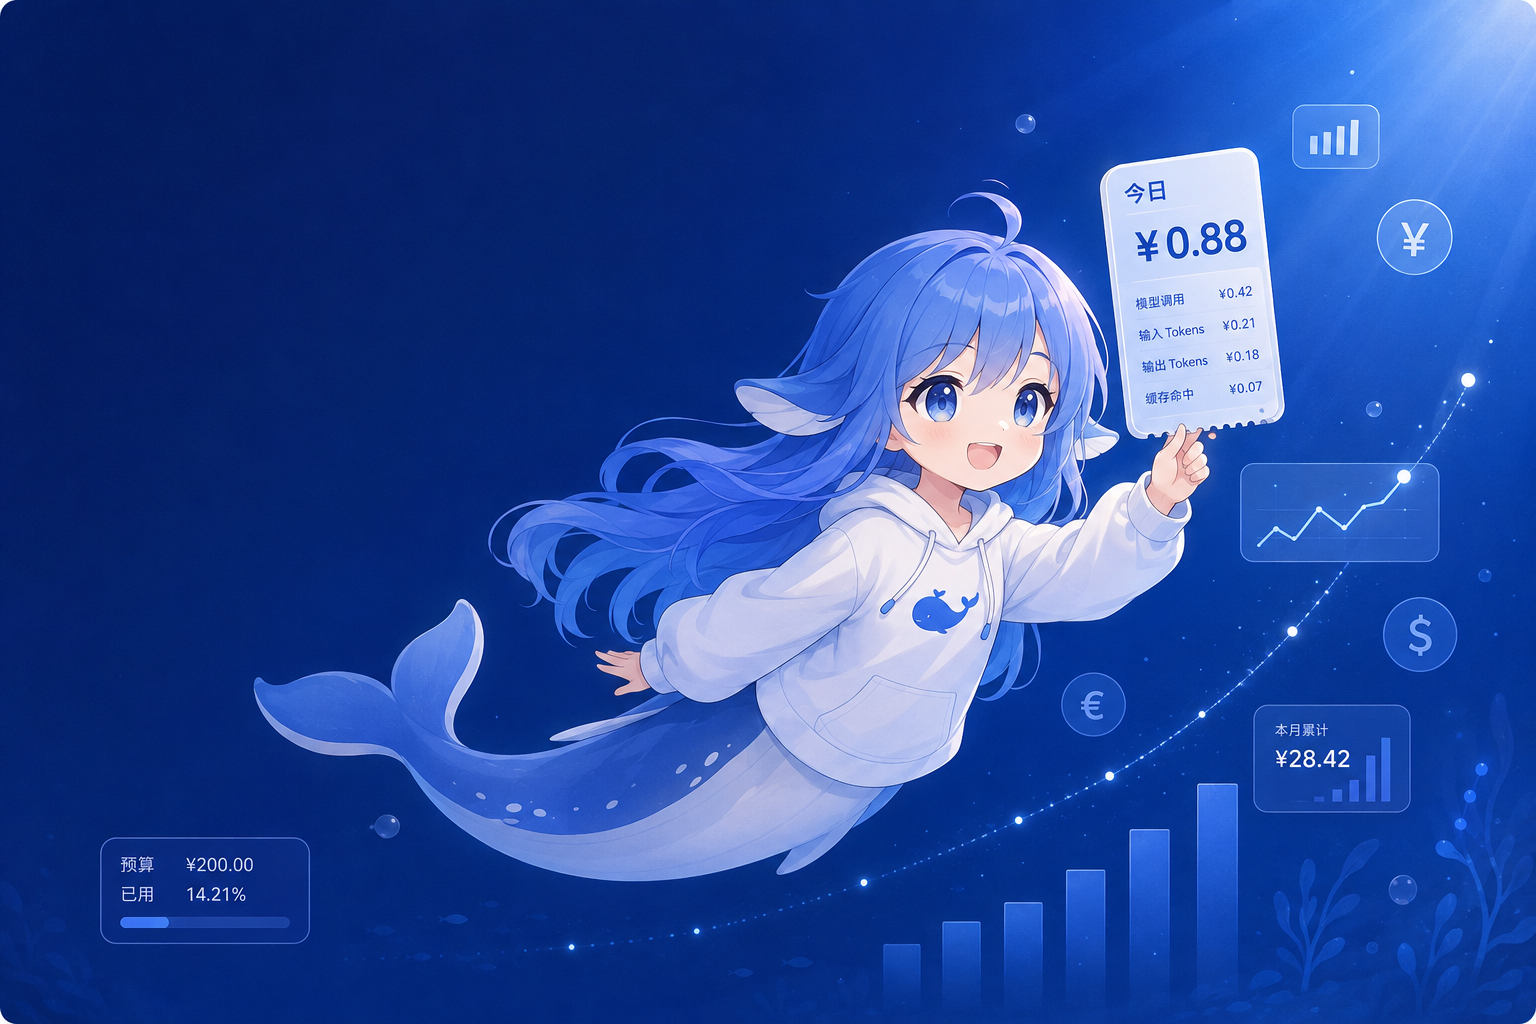
DeepSeek Harness 会话费用统计插件,中英双语界面,支持预算、官方与自定义 Provider 余额、OpenCode Go/Coding Plan 额度、峰谷计价与提醒、历史统计等。